A JavaScript skimmer loading from a fake CSS request to URL printcss[.]host/styles.css which was injected into the Magento 2 database table cms_block.content.
printcss.host Loads JavaScript Skimmer 0x2031
A JavaScript skimmer loading from a fake CSS request to URL printcss[.]host/styles.css which was injected into the Magento 2 database table cms_block.content.
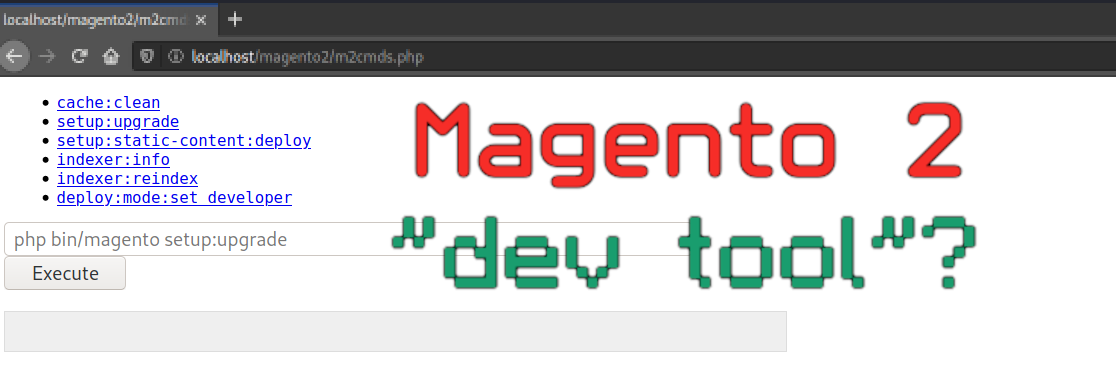
Is this m2cmds.php file an insecure third-party dev tool for Magento - or a malicious hacktool used by an attacker?
A payment card skimmer hidden within an existing PNG image on an infected WordPress website that uses MemberPress and collects payment data for private membership. A variant was also found stealing payment card information on an infected Magento website.

A PHP skimmer injected into a Magento 2 core file and used to steal login data from HTTP requests.
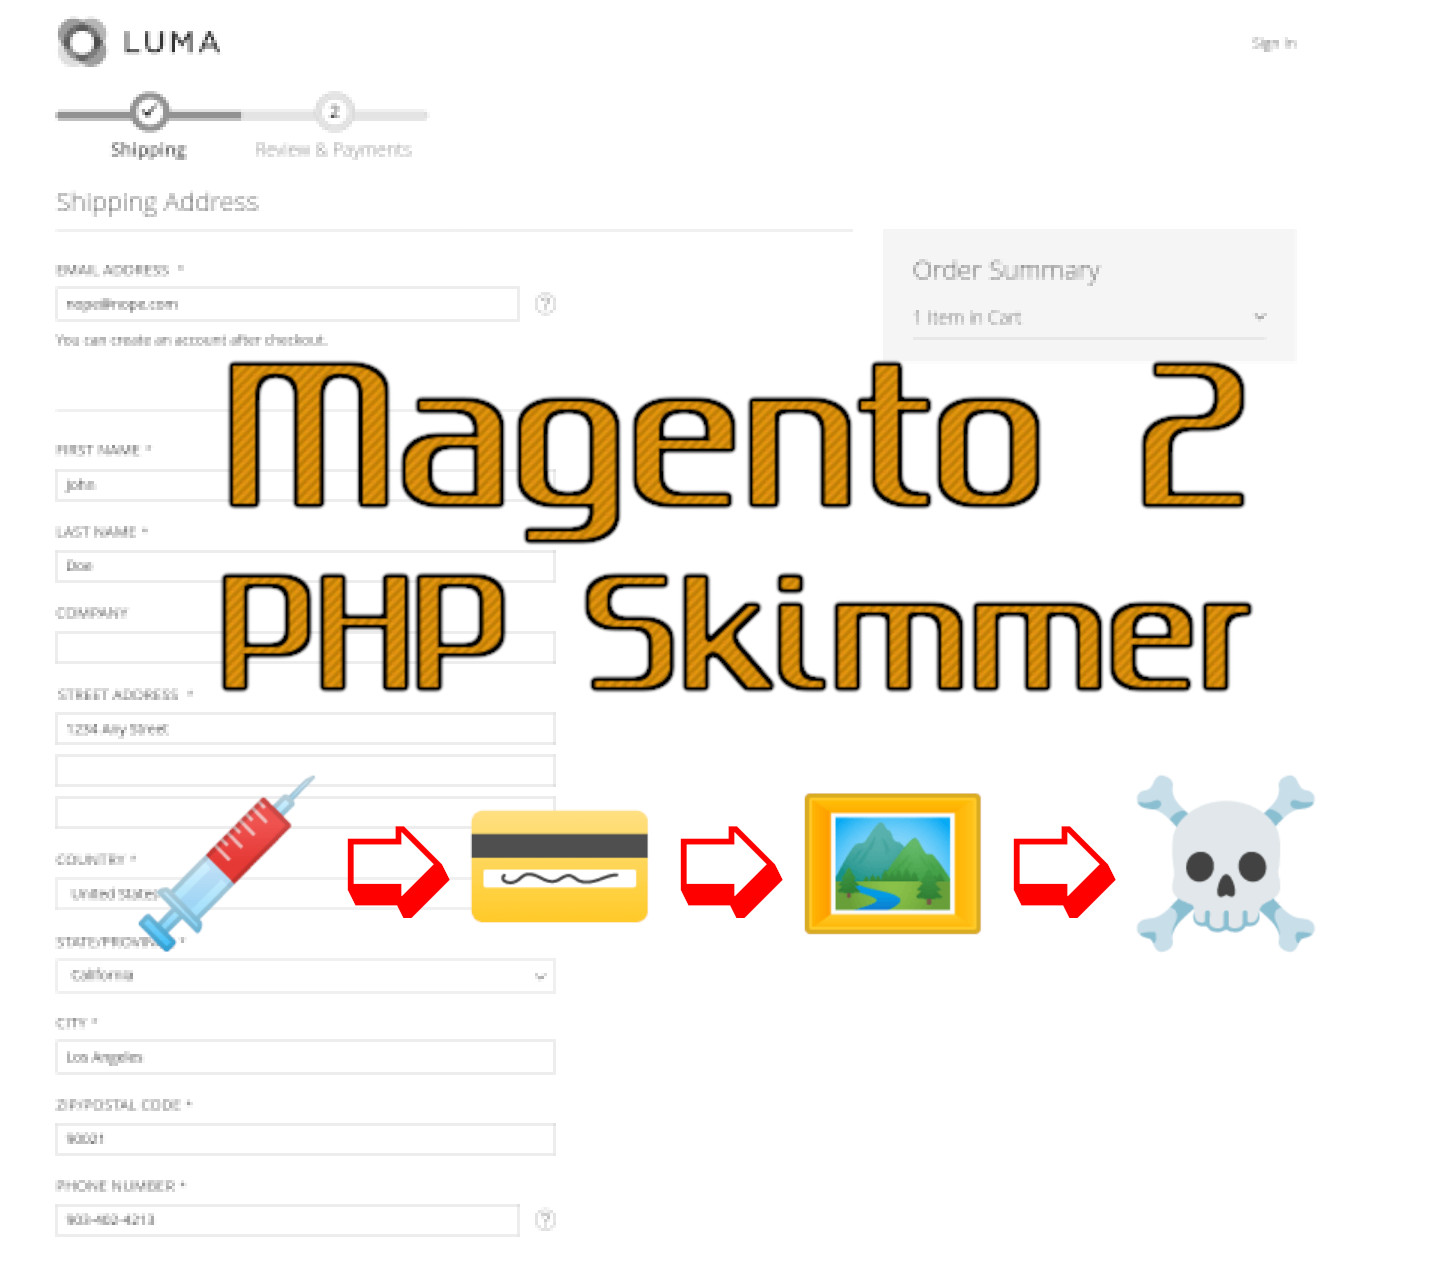
A PHP skimmer injected into a Magento 2 core file that captures POST data on the cart checkout page and saves the stolen data to an image file on the hosting server.

A JavaScript skimmer that conditionally loads from malicious PHP code injected into a Magento file.
It’s important to an attacker for a skimmer to remain undetected for as long as possible, so they do research and use various techniques to make the request that loads the skimmer look innocuous.
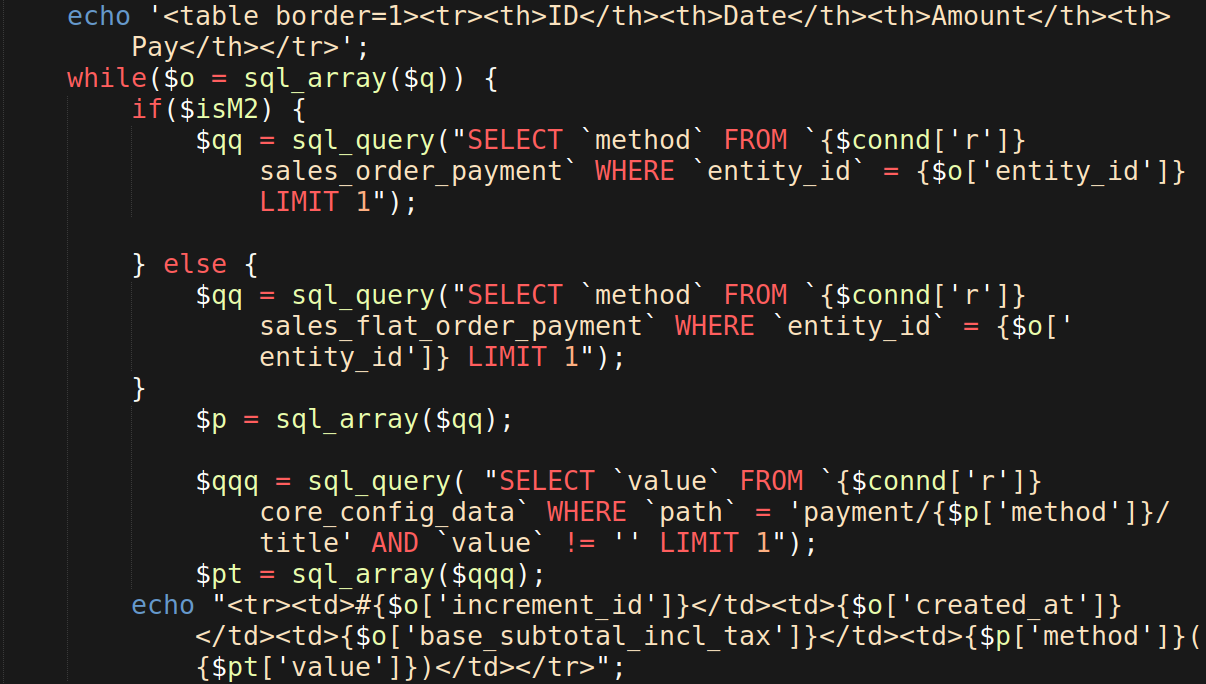
Magento’s continued migration from 1.x to 2.x versions has led malware authors to modify existing malicious tools to accomodate for the major differences between these Magento versions.
Disclaimer: The research posted on this website is for information purposes only. Do not use it for illegal purposes.