How a PHP web shell uses basic functions like tempname, require, and urldecode to remain lowkey.
DarkClownSecurity Web Shell
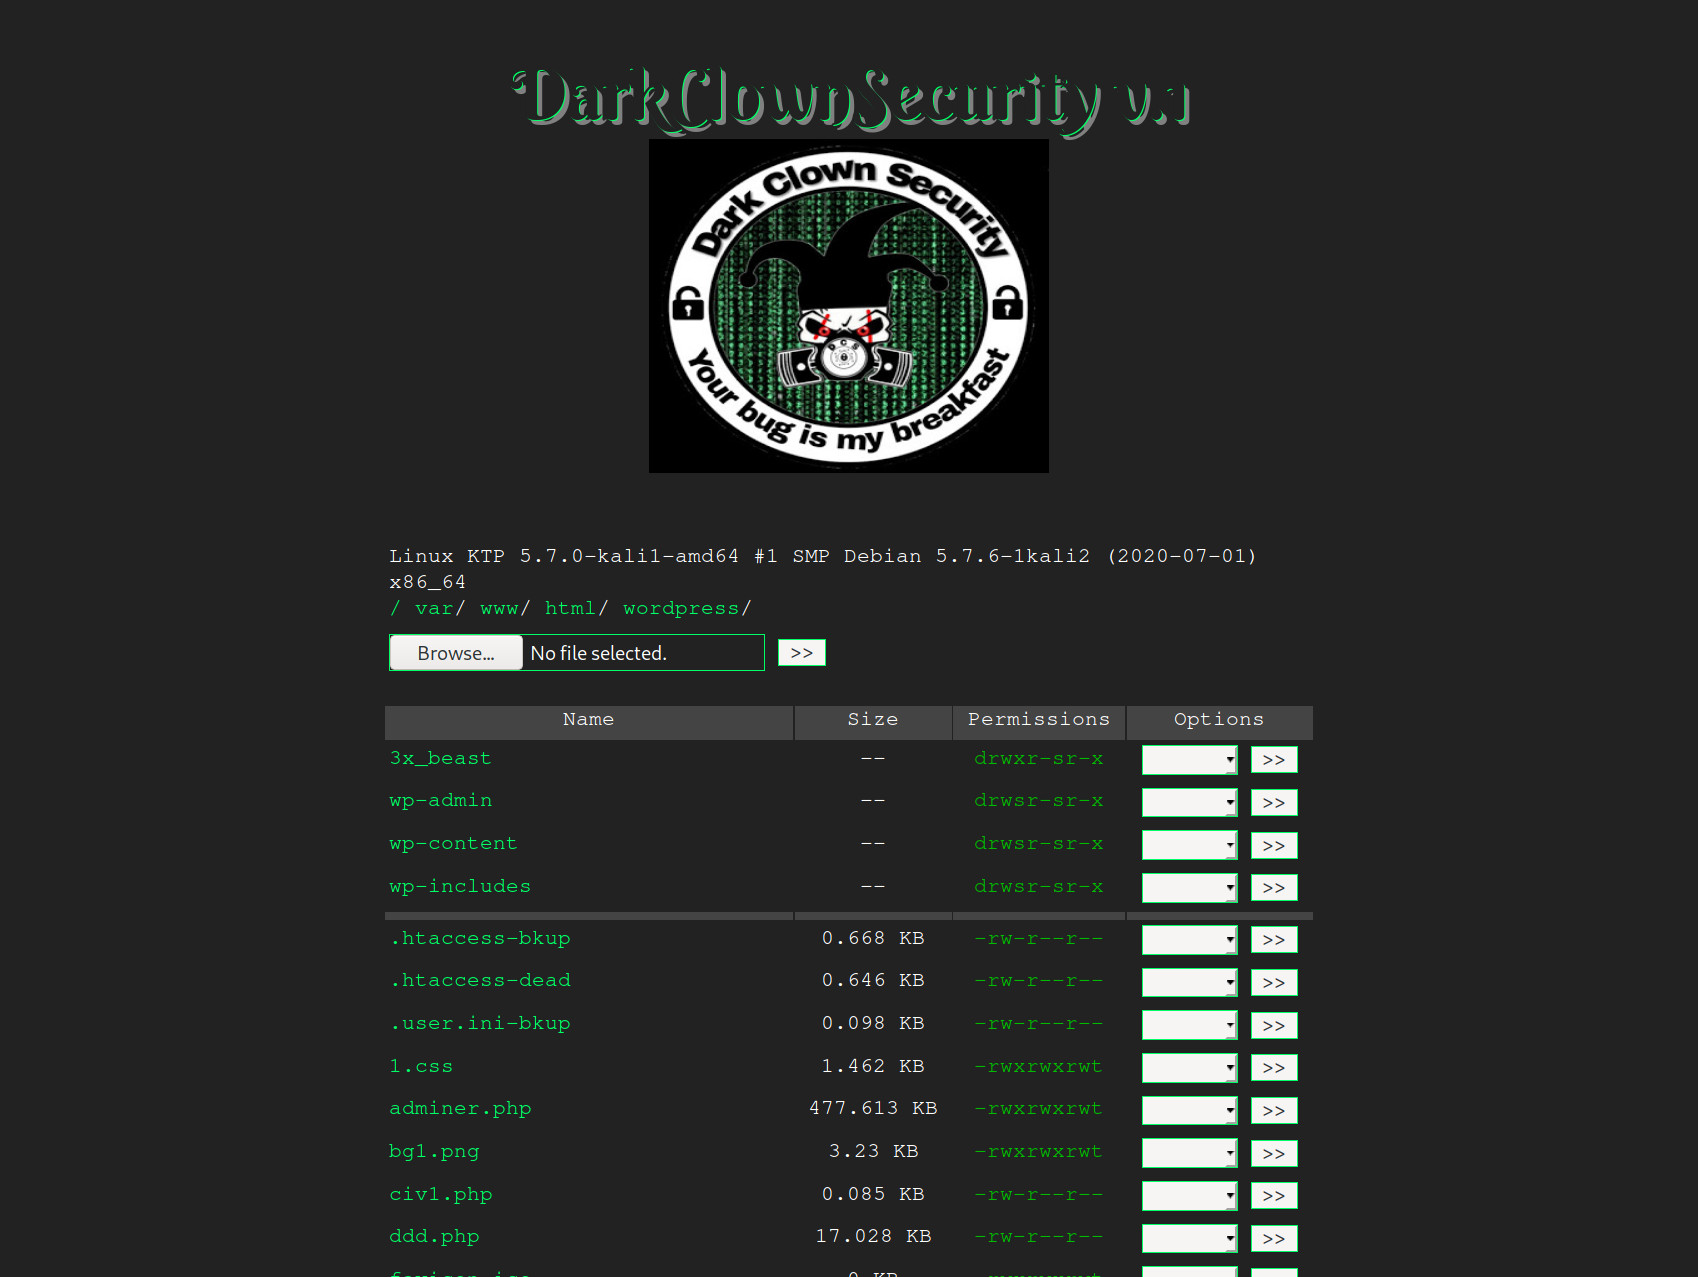
How a PHP web shell uses basic functions like tempname, require, and urldecode to remain lowkey.
A malware injection used to automatically inject a SuperAdmin user into the Prestashop _employees database table.
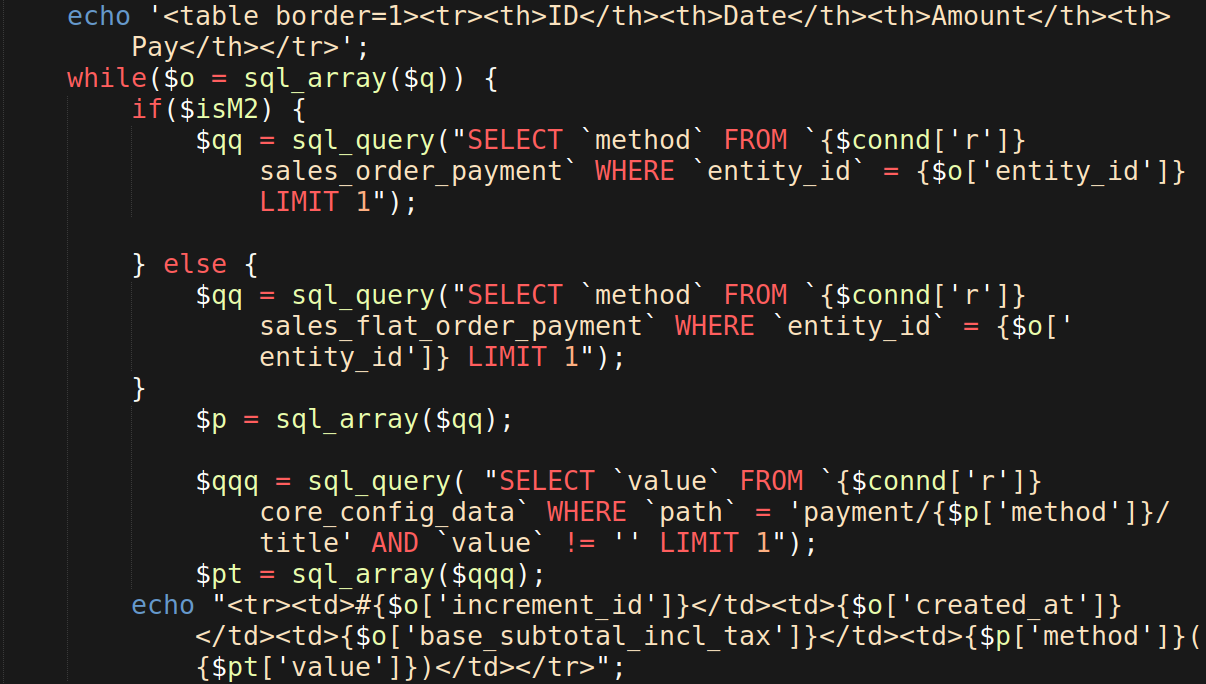
Magento’s continued migration from 1.x to 2.x versions has led malware authors to modify existing malicious tools to accomodate for the major differences between these Magento versions.
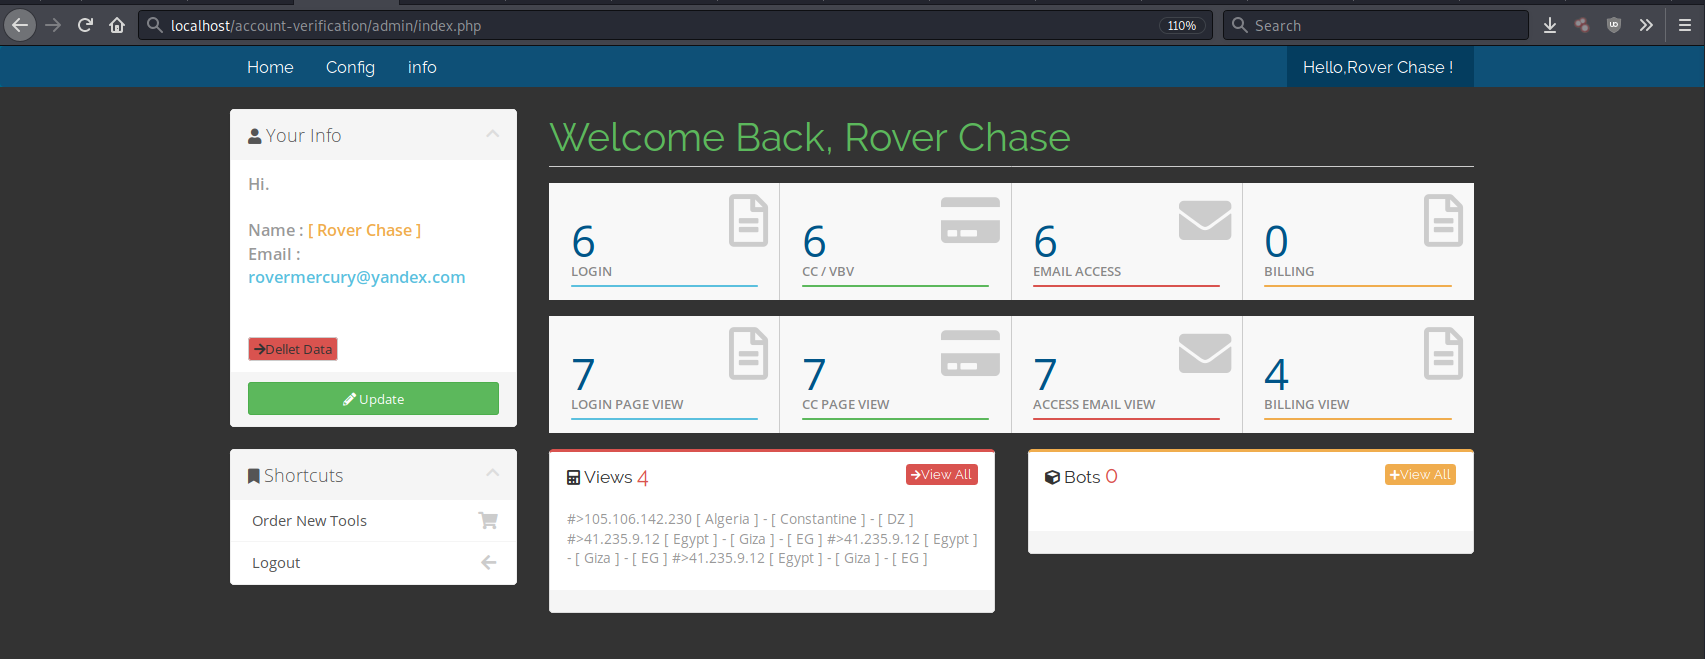
Analysis of a phishing kit and its admin panel used for managing phishing pages that target Chase Bank and other organizations. The kit was created by ‘Spox’.

How do hackers use a PHP backdoor that is injected into a single line of code in a website’s file? Why is it better at evading malware scanners than other PHP backdoors?
Disclaimer: The research posted on this website is for information purposes only. Do not use it for illegal purposes.