A PHP skimmer injected into a Magento 2 core file and used to steal login data from HTTP requests.
Magento 2 Skimmer Uses getCredentialStorage

A PHP skimmer injected into a Magento 2 core file and used to steal login data from HTTP requests.
RansomWeb malware rewrites your file’s text to unreadable binary data and appends .xploiter to the file’s extension (e.g index.php.xploiter) - but you can use the malware against itself to revert back to your original files.
Attackers are using SQL triggers as a backdoor to create a malicious admin user whenever a special comment is submitted to an infected WordPress website.
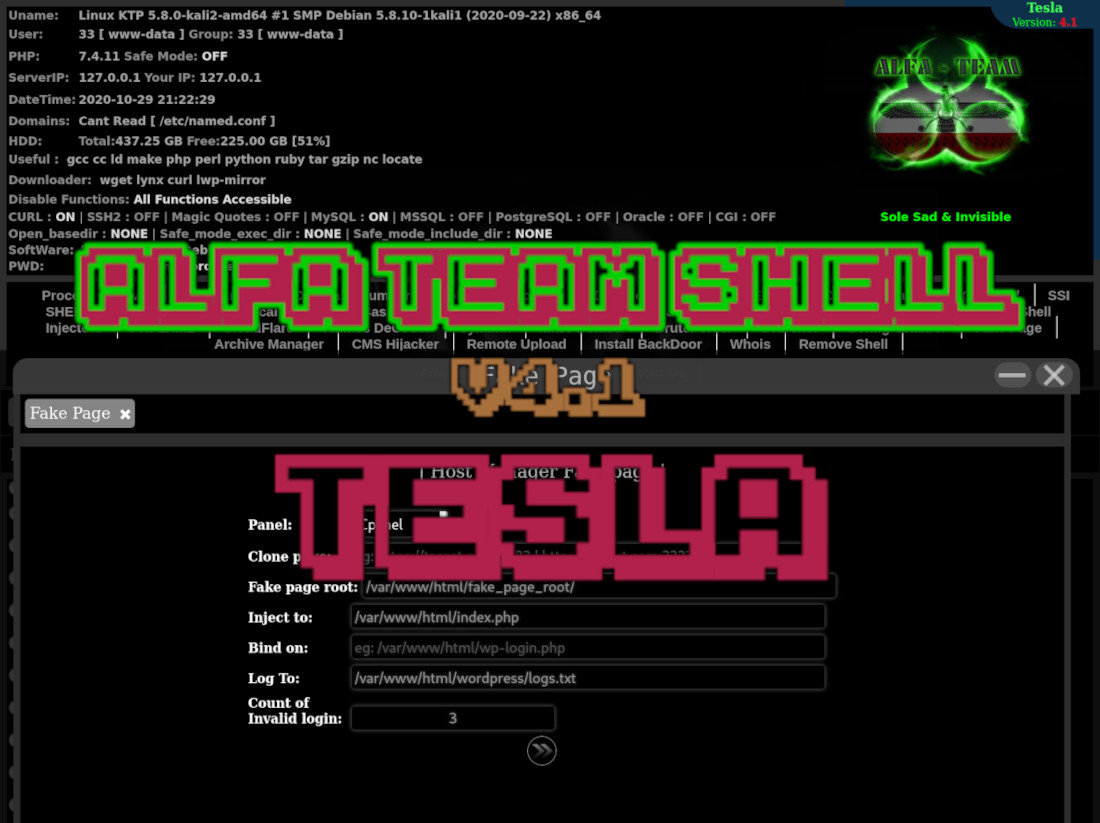
A new PHP web shell by ALFA TEaM that has some interesting new features like the ability to create a cPanel phishing page that blocks the victim from a part of their website until they interact with the phishing page.
How to load/execute malicious PHP code stored in HTTP cookie values.
Disclaimer: The research posted on this website is for information purposes only. Do not use it for illegal purposes.