A malicious PHP file is used to take down Wordfence plugin before it adjusts its own mtime timestamp.
Malware Disables Wordfence Security Plugin & Forges Timestamps
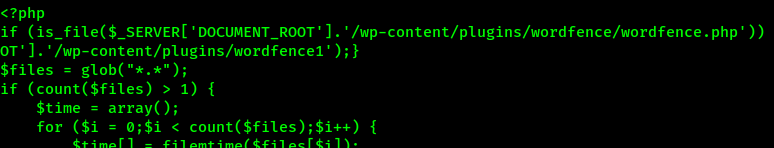
A malicious PHP file is used to take down Wordfence plugin before it adjusts its own mtime timestamp.
A PHP backdoor that injects its payload into the default PHP error_log
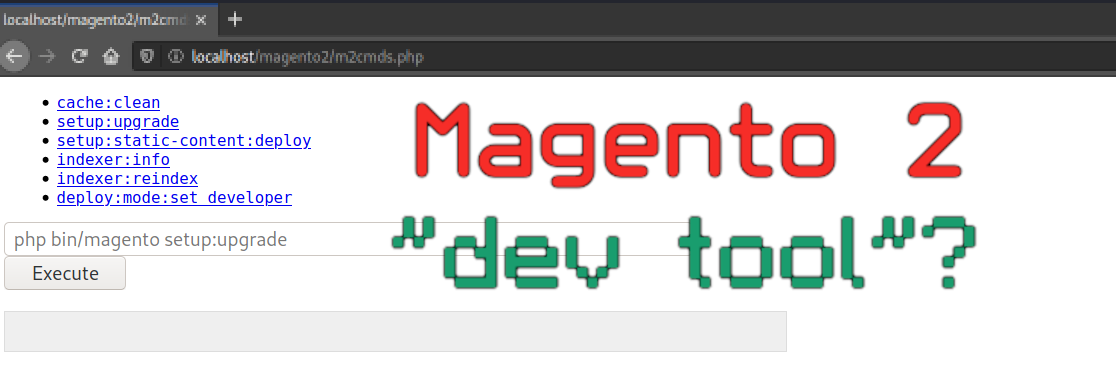
Is this m2cmds.php file an insecure third-party dev tool for Magento - or a malicious hacktool used by an attacker?
A payment card skimmer hidden within an existing PNG image on an infected WordPress website that uses MemberPress and collects payment data for private membership. A variant was also found stealing payment card information on an infected Magento website.
Attackers were running recon on a foreign company via trojan spyware connected to a C2 panel on a compromised web host server. Unfortunately they forgot to have their logs and screenshots automatically purged from their C2 panel, so I was able to stumble upon their mainly intact C2 panel. Let’s see what it reveals about their operation.
Disclaimer: The research posted on this website is for information purposes only. Do not use it for illegal purposes.